ProductPRODUCT
Featured products
Contact Us
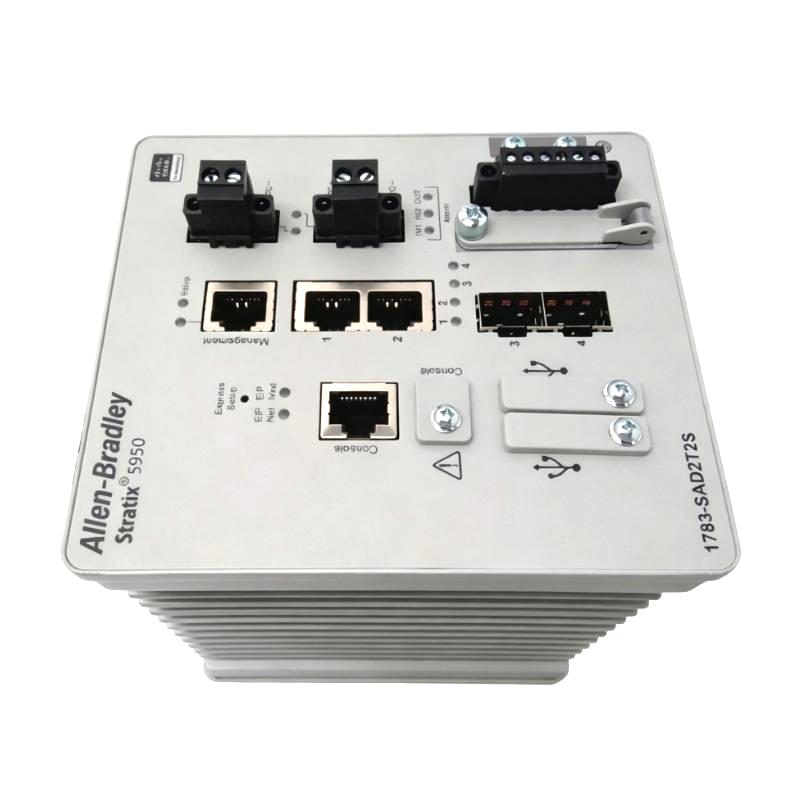
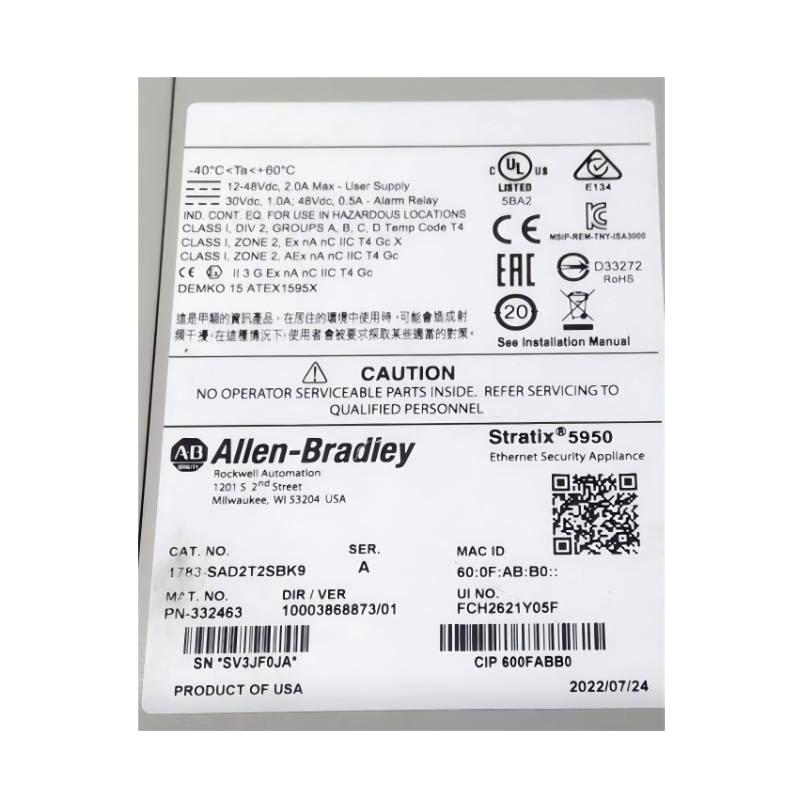
- Allen Bradley
- 1783-SAD2T2SBK9
- Security Appliance
- USA
- 159.26 × 106.68 × 129.54 mm
- 0.9 kg
- Xiamen, China
- New & In Stock
- T/T, PayPal, Western Union
- 1 Year
- 1-3 Working Days
- DHL, UPS, TNT, FedEx and EMS.
- 24-Hour Service
- COO
- 4
Our advantage
Global Logistics
We have a 10-year logistics and express cooperation agreement, so our products can be shipped to any place in the world.
Brand new and original
Our products are imported in bulk from the place of origin. Because of the cooperative relationship, our products are all original and 100% new.
24-hour service
We provide 7*24 hours service to our customers. We will be there whenever you need us.
Price advantage
All our products are priced very favorably because we have our own warehouse and supply.
| Company Information | |||
| [email protected] | |||
| Mobile | +8615980777398 | ||
| +8615980777398 | |||
| 15980777398 |
Product Overview
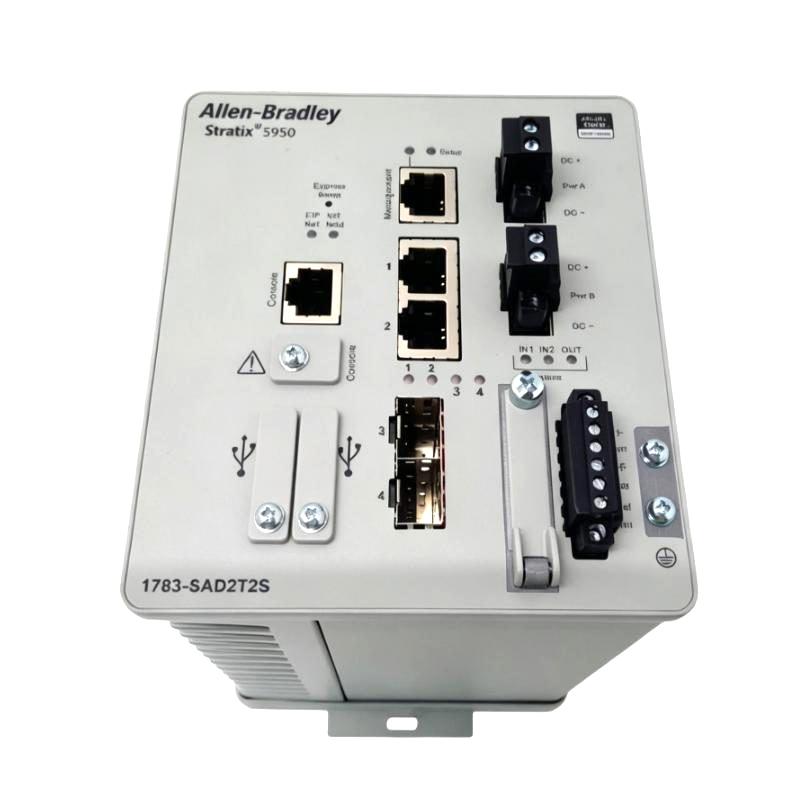
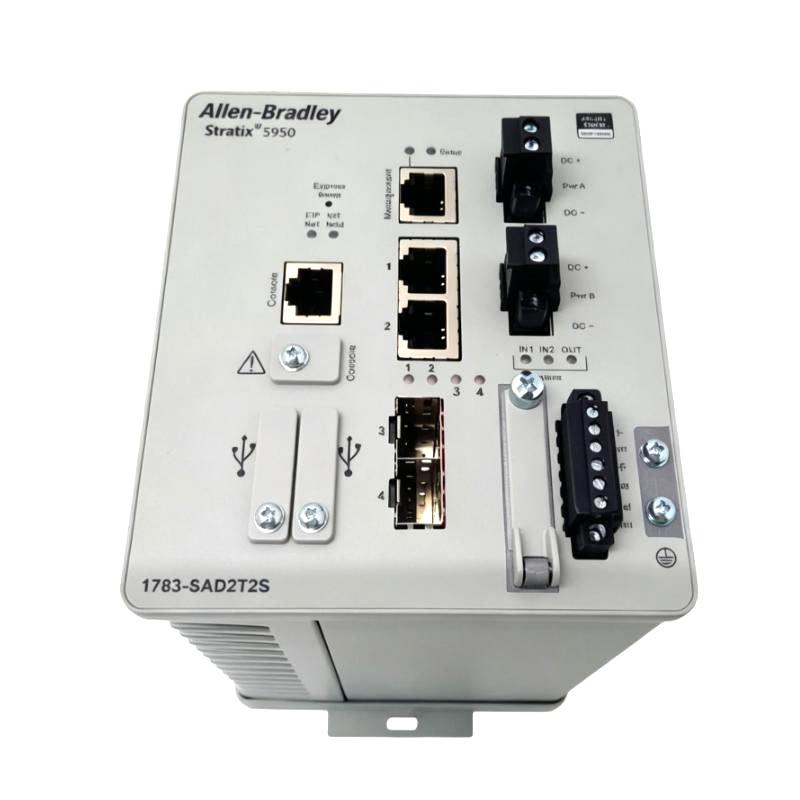
The Allen Bradley 1783-SAD2T2SBK9 Stratix 5950 Security Appliance is an industrial network security device used to protect communication between automation equipment and other network segments. In a manufacturing facility, it may be deployed at the boundary between a plant-floor control network and an enterprise network, where traffic needs to be controlled rather than passed freely between systems.
Industrial networks often connect PLCs, HMIs, engineering workstations, supervisory systems, and remote maintenance infrastructure. While these connections support production and diagnostics, they also create paths that need appropriate security controls. A Stratix 5950 security appliance can form part of the network architecture used to regulate traffic and separate control-system resources from other parts of the organization’s network.
For system integrators and plant engineers, placement and configuration are as important as the physical installation. The appliance should be incorporated into a defined network topology, with communication rules based on the devices and services that actually need to exchange data. Its role is network protection; PLC control logic and machine sequencing remain the responsibility of the automation controllers.
Technical Specifications
| Parameter | Specification |
|---|---|
| Manufacturer | Allen-Bradley |
| Model | 1783-SAD2T2SBK9 |
| Product Family | Stratix 5950 |
| Product Type | Security Appliance |
| Device Category | Industrial Network Security Equipment |
| Primary Function | Industrial network security and traffic control |
| Network Application | Industrial Ethernet security |
| Typical Deployment | Boundary between industrial network segments |
| Connected Equipment | Controllers, HMIs, switches, and other network devices, subject to configuration |
| System Role | Network protection and segmentation |
| Installation Context | Industrial control cabinet or suitable equipment enclosure |
| Security Configuration | Depends on the deployed network design and supported features |
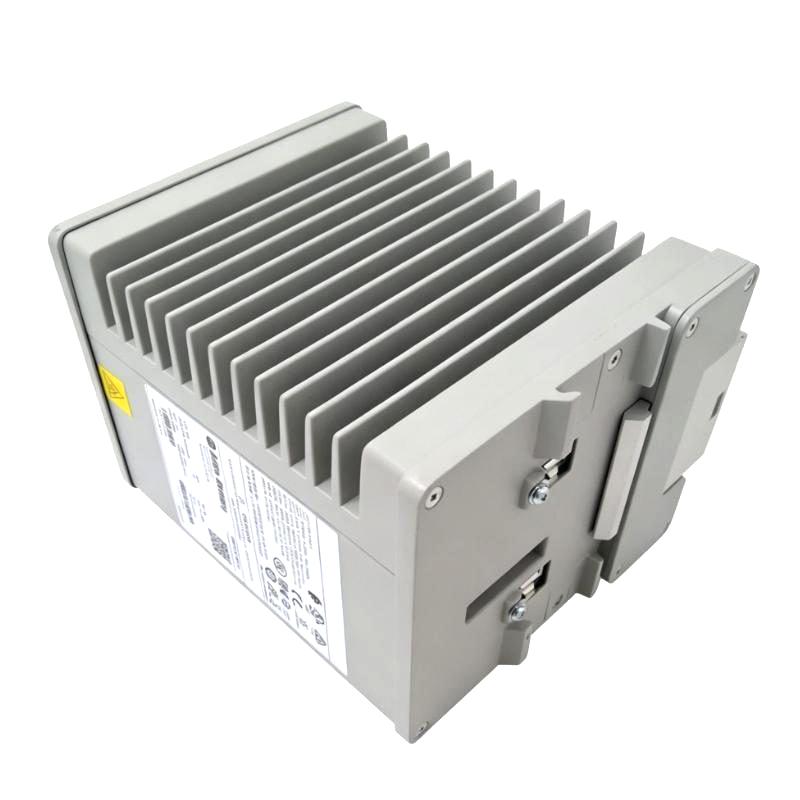
| Dimensions | 159.26 × 106.68 × 129.54 mm |
| Weight | 0.9 kg |
Product Features
- Industrial network protection: Supports security arrangements for networks used by automation equipment.
- Stratix 5950 platform: Belongs to Allen-Bradley’s industrial network security product family.
- Traffic control: Can be incorporated into a configuration that regulates communication between designated network segments.
- Network segmentation: Helps establish boundaries between control-system resources and other connected networks.
- Automation infrastructure integration: Can be deployed alongside industrial Ethernet switches, PLCs, HMIs, and supervisory systems.
- Policy-based operation: Security behavior depends on the appliance’s supported capabilities and the rules established during configuration.
- Industrial maintenance support: A documented security configuration helps technicians investigate blocked connections and communication problems.
- Layered security architecture: Can form one part of a broader approach that also includes access controls, secure engineering practices, and network monitoring.
Working Principle
The 1783-SAD2T2SBK9 operates within the network path between connected segments. Rather than functioning as a PLC or a standard endpoint device, it applies the network security functions configured for the installation.
Consider a production facility where PLCs and HMIs communicate over a plant-floor network while engineering and supervisory systems connect through another network segment. The security appliance can be placed at the boundary between these segments so that permitted communication is allowed and other traffic is restricted according to the configured policy.
A simplified network path is:
Enterprise / Supervisory Network → Stratix 5950 Security Appliance → Industrial Control Network → PLCs / HMIs / Automation Devices
The precise traffic-handling behavior depends on the appliance’s supported features, operating mode, and security configuration. Engineers need to account for the communication protocols and services required by the control system. Overly restrictive rules can interrupt legitimate PLC, HMI, engineering, or diagnostic traffic, while overly permissive rules can weaken the intended network boundary.
For this reason, security changes should be tested against the actual application and documented so that later maintenance does not unintentionally disrupt production communication.
Role in an Industrial Network Security Architecture
The 1783-SAD2T2SBK9 serves as a security element between network segments in an industrial automation environment. Its purpose is to help control which communication paths are available to connected systems, according to the deployed configuration.
Enterprise / Supervisory Network → 1783-SAD2T2SBK9 → Industrial Ethernet Network → PLC / HMI / Control Devices
| System Element | Function |
|---|---|
| 1783-SAD2T2SBK9 Stratix 5950 | Provides the configured industrial network security functions |
| Industrial Ethernet Switch | Connects devices within the control network |
| Allen-Bradley PLC | Executes machine or process control logic |
| HMI | Displays machine status, alarms, and operating information |
| Supervisory System | Collects production data and supports higher-level monitoring |
| Engineering Workstation | Runs controller configuration and diagnostic software |
| Enterprise Network | Supports business systems and authorized connections to plant resources |
| Network Monitoring Tools | Help identify communication anomalies and diagnose network issues |
The final architecture depends on the required communication paths, network topology, security policies, and supported appliance capabilities. Not every system element listed above is required in every installation.
Industrial Applications
| Application | Typical Use | Role in Network Security |
|---|---|---|
| Factory Automation | Separating control devices from other network segments | Limits unnecessary communication paths |
| Manufacturing Plants | Controlling traffic between production and supervisory networks | Establishes a defined network boundary |
| Packaging Lines | Protecting communication paths for controllers and operator interfaces | Supports controlled access to automation resources |
| Process Automation | Regulating communication between control and monitoring systems | Helps enforce network segmentation |
| Machine Builder Installations | Integrating security boundaries into machine network designs | Supports structured access to machine resources |
| Industrial System Integration | Implementing network separation during commissioning | Aligns communication paths with system requirements |
| Multi-Segment Control Networks | Controlling traffic between different automation areas | Reduces unrestricted communication between segments |
| Industrial Maintenance Networks | Restricting access to designated engineering and diagnostic resources | Supports controlled maintenance connectivity |
Installation and Maintenance
- Confirm the complete model number, 1783-SAD2T2SBK9, and identify its intended position in the industrial network architecture.
- Document the existing network topology, including the control devices and network segments that will communicate through the appliance.
- Isolate the relevant power supply before installation or wiring, following the site’s electrical safety procedures.
- Check the mounting location and confirm that the installation environment meets the applicable product requirements.
- Mount the appliance securely and maintain sufficient access to its connections and status indicators.
- Connect the network interfaces according to the approved network diagram and intended traffic paths.
- Verify the power connections and applicable grounding arrangements before energizing the equipment.
- Configure the appliance according to the planned network addressing, operating mode, and security policy.
- Define communication rules around the services and devices required for production, engineering, and maintenance.
- Test permitted and restricted traffic paths in a controlled manner before placing the configuration into normal operation.
- If communication fails, check interface status, cabling, addressing, policy rules, and the affected devices’ required network services.
- Record the final configuration, approved communication paths, and maintenance changes so that future troubleshooting can be performed consistently.
If a controller or HMI becomes unreachable after a security change, compare the affected communication path with the configured rules and the device’s actual network requirements. Test changes in a controlled manner and avoid disabling security controls indiscriminately to restore connectivity.
Related Components
| Component | Function |
|---|---|
| Allen-Bradley Stratix Industrial Ethernet Switch | Connects devices within an industrial network |
| Allen-Bradley CompactLogix PLC | Executes machine-level control logic |
| Allen-Bradley ControlLogix PLC | Controls larger machine and process automation systems |
| Allen-Bradley PanelView HMI | Provides operator access to machine information and controls |
| Industrial Ethernet Cabling | Connects network equipment and automation devices |
| Engineering Workstation | Supports PLC programming, configuration, and diagnostics |
| Supervisory Control System | Collects operating information and supports higher-level monitoring |
| Network Monitoring Tools | Assist with communication analysis and security troubleshooting |
Recommended Related Models
| Model / Product Family | Product Type | Application Context |
|---|---|---|
| Allen-Bradley Stratix 5950 | Industrial Security Appliance | Network security for industrial automation environments |
| Allen-Bradley 1783-RMS06T | Stratix 8300 Ethernet Switch | Local industrial Ethernet connectivity |
| Allen-Bradley Stratix 5700 | Managed Industrial Ethernet Switch | Industrial network connectivity and management |
| Allen-Bradley Stratix 5400 | Managed Industrial Ethernet Switch | Industrial network aggregation and distribution |
| Allen-Bradley CompactLogix 5380 | Programmable Automation Controller | Machine-level automation and control |
| Allen-Bradley ControlLogix 5580 | Programmable Automation Controller | Larger machine and process control applications |
| Allen-Bradley PanelView 5000 | Operator Interface Terminal | Local operation and monitoring of automation equipment |
Key Advantages
- Supports controlled communication between industrial network segments.
- Helps establish security boundaries around automation equipment.
- Can be integrated into a layered industrial cybersecurity architecture.
- Allows communication rules to be aligned with actual control-system requirements.
- Supports structured troubleshooting through documented network policies and connection paths.
Technical FAQs
1. What is the main function of the Allen-Bradley 1783-SAD2T2SBK9?
The 1783-SAD2T2SBK9 is identified as a Stratix 5950 Security Appliance. It is used in industrial networking environments to support network security and controlled communication between connected network segments.
2. How does a security appliance differ from an industrial Ethernet switch?
An Ethernet switch primarily connects network devices and forwards traffic between them. A security appliance applies configured security functions to communication paths, helping regulate which traffic is permitted between designated network segments.
3. Can installing the appliance affect PLC or HMI communication?
Yes. If required communication is not included in the security configuration, traffic between a PLC, HMI, engineering workstation, or supervisory system may be blocked. The network rules should account for the protocols and services needed by the application before the appliance is placed into normal operation.
4. What should be checked if devices stop communicating after a security configuration change?
Check the relevant interfaces, network addressing, configured security rules, and the communication services required by the affected devices. Compare the failed connection with the intended network policy to determine whether the issue is caused by an incorrect rule or another network fault.